Wide Open: Hundreds of MCPs Exposing Root Shells, Production Data, and Citizen Records One Call Away

Pluto Research found 179 exposed MCP server deployments across the internet. 147 accepted unauthenticated requests, exposing everything from root access and production credentials to financial data and municipal citizen workflows.
Read More

Inside Claude Code Function Hooks: The Trust Problem Behind Claude Mods

Pluto Research tested Claude Code’s new function-hook model and found four trust gaps, including silent secret access, missing capability disclosure, UI spoofing, and code that…

A Security Leader’s Guide to Latio’s 2026 AI Security Market Report

A practical breakdown of Latio’s 2026 AI Security Market Report, what security leaders should look for, and why Pluto was recognized as an Endpoint AI…
Read More

MCP Through an Attacker’s Eyes: The New Path Into Enterprise Environments

A working exploit for MCPfluence appeared on a cybercrime forum just 20 days after responsible disclosure. Pluto Research traces the attack path, examines similar exploitation…
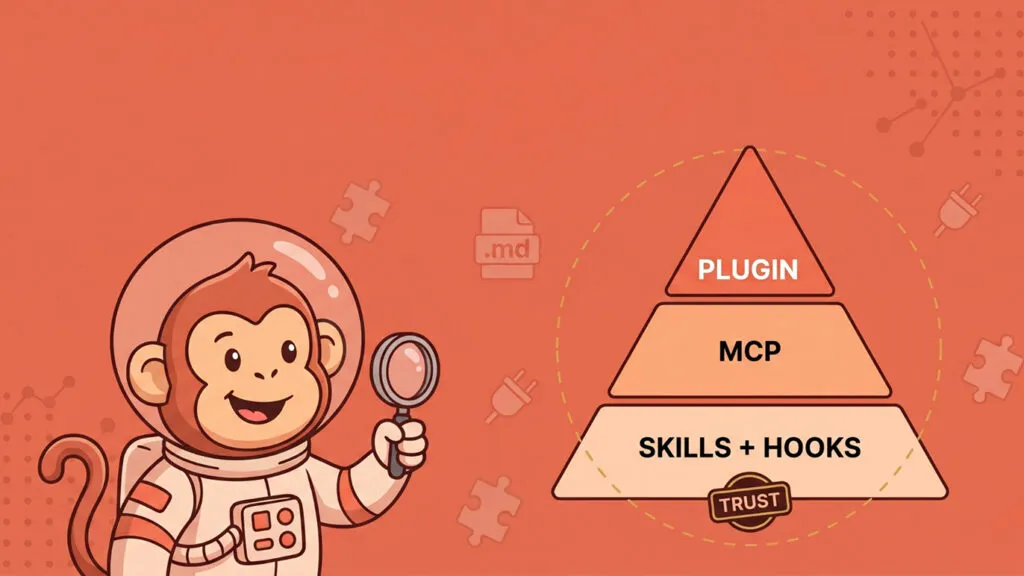
Malicious Servers, Clean Scans: The Dangerous Illusion of a Clean MCP Scan

Pluto Research tested five public MCP security scanners against malicious servers. Several returned clean or zero-finding results, exposing the gap between what a scan checks…

Introducing MCP Inspector: Know an MCP Server’s Risks Before You Install It

Meet MCP Inspector, a free tool from Pluto Research that checks MCP servers for security risks before you install them. Built from the findings behind…

Your CI Pipeline Is a Credential Vending Machine: 7 Lessons from the TeamPCP supply-chain attacks

TeamPCP turned trusted automation into a path for credential theft and lateral compromise. Based on 37 mapped incidents, here are seven controls defenders should prioritize…